How to Use the Investigate Interface
The Investigate interface provides a convenient means of filtering and examining your customer data.
You can access numerous preset investigations or saved queries, the results of which can then be further filtered and refined. You can customize the time range of an investigation to any range within the last 30 days, and can filter the information on very specific criteria.
For example, you could use investigations to isolate and review low or non-security information to find ways to fine-tune configurations and network processes. With investigations, you can independently verify the traffic and system behaviors that the SOC monitors 24/7.
The sections in this topic will describe the functions of the Investigate interface, and present an example of how a specific investigation can be conducted.
Overview of the Investigate Landing Page
To access the Investigate landing page, click Investigate in ActiveEye’s left navigation pane. The primary purpose of the Investigate landing page is to access investigation results pages, either by selecting a query in the My Saved Queries section, or by selecting a preset investigation in the Preset Investigations section. Familiarize yourself with the important page elements noted in the following image and descriptions, and then continue to the next section of this topic for an example of how to begin a specific investigation.
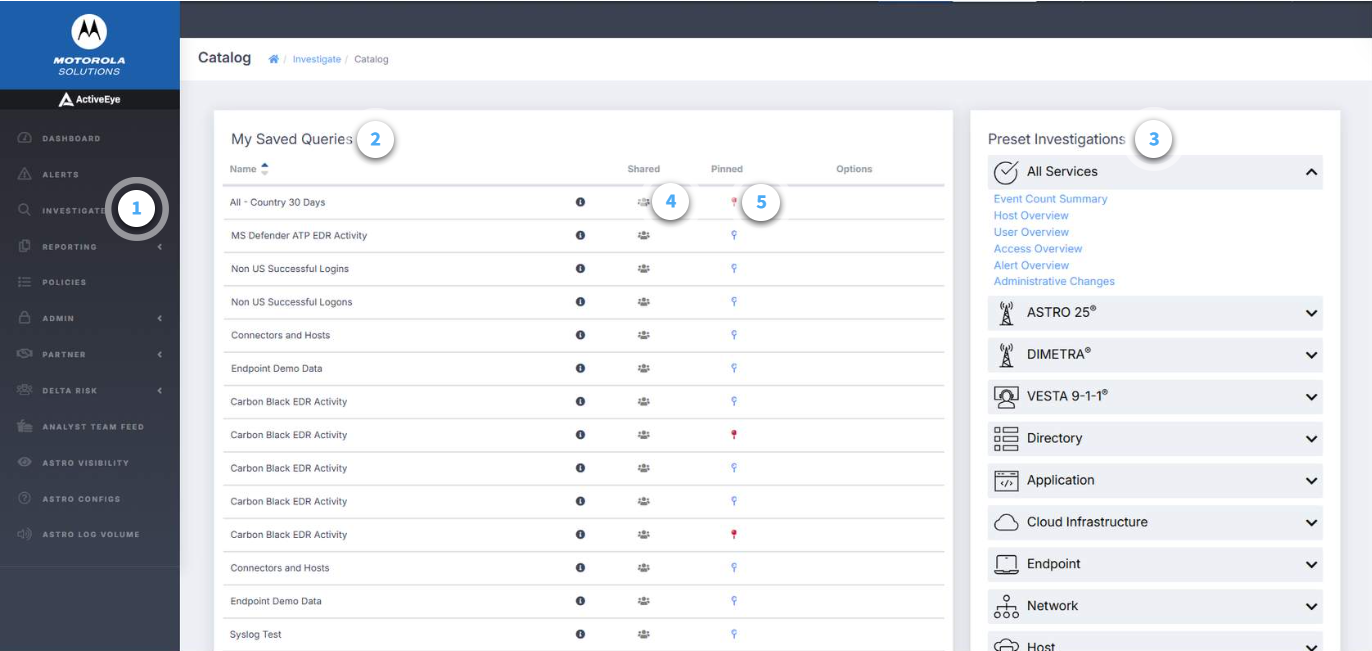
- Investigate Left Navigation Button: Click this button to access the Investigate landing page.
- My Saved Queries: The My Saved Queries section displays filtered investigations that you have saved, or that someone in your organization has shared. The table provides a means to readily access these queries. Select a query in the table to access its investigation results.
- Preset Investigations: Preset investigations are created by ActiveEye Engineering. They are organized into several drop-down lists. Each set of preset investigations provides insight into a different ActiveEye feature. Select a preset investigation to access its investigation results.
tip
You can hover over any preset investigation name to display a description of the types of data that it returns.
- Shared State: In the table, icons in the Shared column represent the shared state of saved queries. The single-person icon indicates that the query was saved by you, and is not shared. The multiple-person icon indicates that the query was shared by someone else in your organization.
tip
If you hover over a multiple-person icon, the name of the person who shared the query will be displayed.
- Pinned Investigations: If you have been assigned the Admin role (see the ActiveEye Capabilities by User Role topic), you can pin any query in the My Saved Queries section, causing it to appear on the main Dashboard landing page of everyone in your organization. To pin an investigation, switch the toggle in the Pinned column in the row for the saved query that you want to pin or unpin. A red pin icon indicates that the saved query is pinned, and a blue pin icon indicates that it is not.
Example Investigation: Beginning an Investigation
Let’s consider an example investigation where we want to find data related to internal network traffic communicating with non-US public IPs between two dates.
To best understand these tutorial example steps, you should follow along and complete each step in your ActiveEye environment. While the data you return with your investigation will be different from what is presented in this topic, the steps required to set up the investigation are the same.
To begin, on the Investigate landing page, we will want to access a preset investigation that will serve as a starting point. In the Preset Investigations section, if you expand the Network subsection, a preset investigation named Network Overview will be revealed.
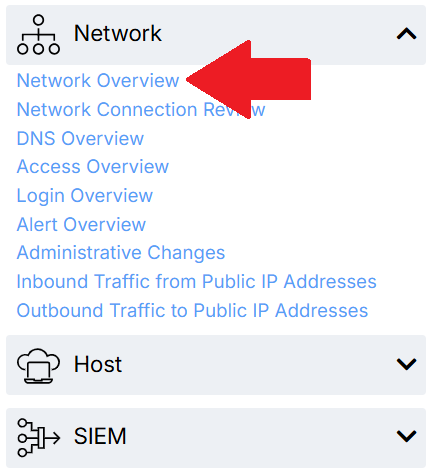
The Network Overview preset investigation returns network activity data with breakdowns by Threat Category, Source IP, Source Country, Destination IP, and Destination Country. This serves as a good base for our example investigation, as it automatically returns data related to network traffic.
Click the Network Overview preset investigation to continue to the Investigate results page.
Overview of the Investigate Results Page
The Investigate results page displays information based on the selected query or preset investigation. These results can then be further refined through additional filtering. Familiarize yourself with the important page elements noted in the following image and descriptions.
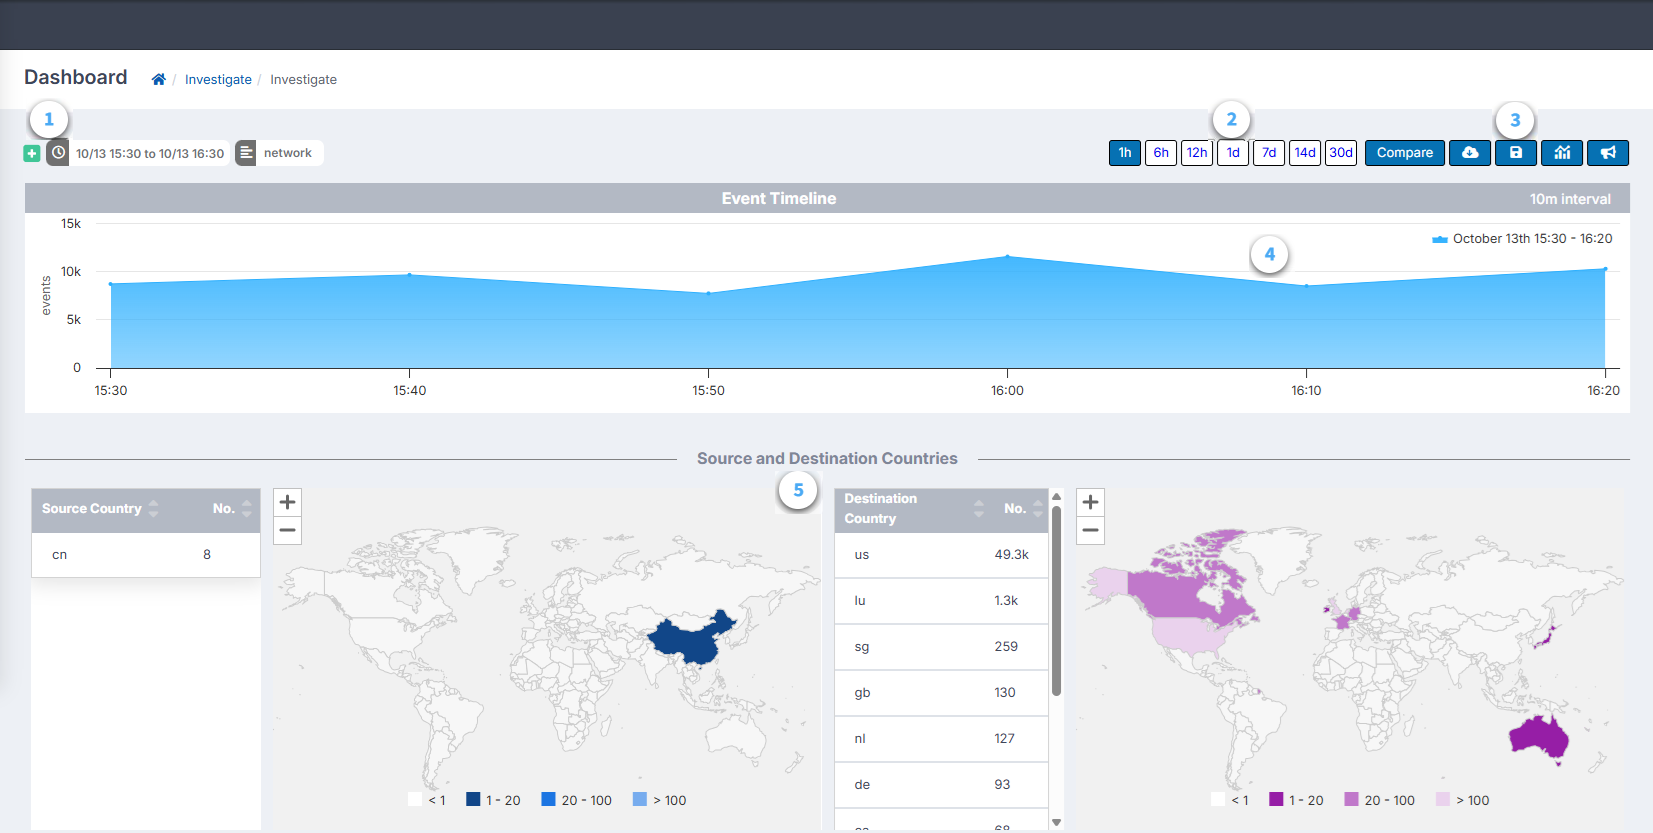
- Adding Filter Criteria to Search: In the upper-left corner of the page, filters active in the selected preset investigation or saved query are displayed. Hovering over each filter reveals options to modify or delete the filter. To add an additional filter, click the
 button, then enter the specifications for the filter, and then click Add Filter.
- Preset Time Range Options: To quickly change the range of time displayed, click any of these buttons displaying an hour or day range.
- Utility Panel Actions: The utility panel actions allow you to compare timelines, download and save data, and include data in reports. These actions will be discussed in more detail in a subsequent section.
- Event Timeline: You can interact with the timeline, adjust the range of dates displayed, and compare it to a second timeline.
- Source and Destination Countries Maps: These maps display the source or destination locations of events, if applicable to the query. You can hover your cursor over a country in the map to reveal detailed information pertaining to that country.
If you scroll further down the Investigate results page, you will find the Field Summary section, as seen in the following image.
The first set of tables display important aggregate information, and can be used to apply additional filtering. The large table at the bottom of the page displays corresponding events, and the Table section of an expanded event can also be used to apply additional filtering. These elements will be discussed in more detail later.
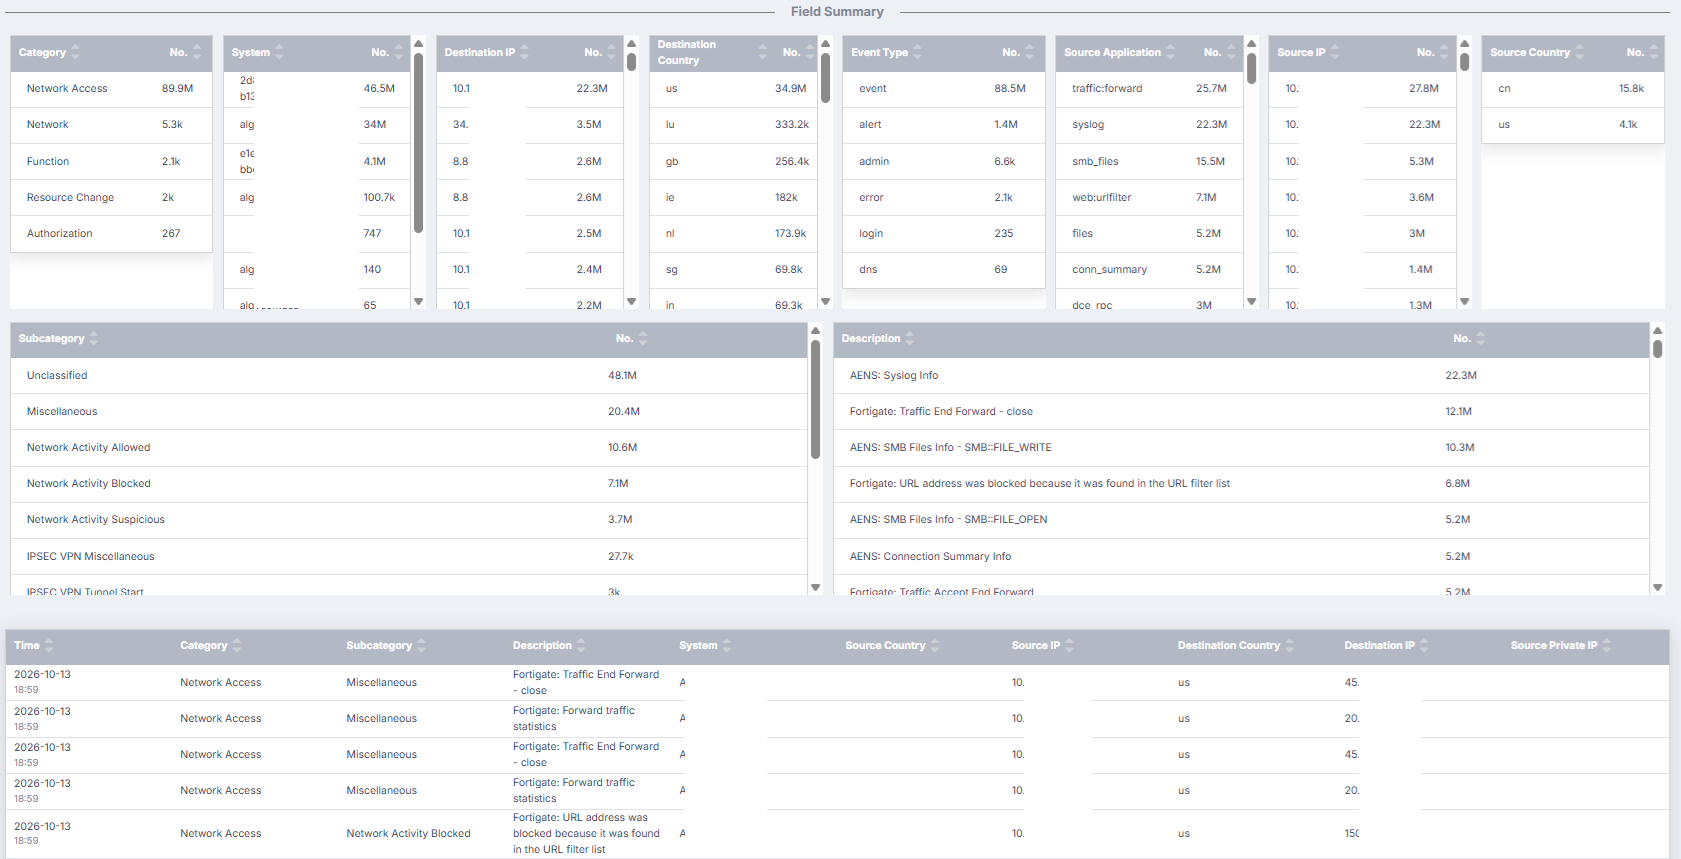
Next, filters can be added or modified to refine the results. Continue to the next section to learn how to further filter the investigation to return the specific data called for in our example investigation.
Example Investigation: Refining Investigation Results
When you access the Network Overview preset investigation, two filters are active (as seen in reference 1 of the first image in the previous section). Hovering over a filter reveals the  button. Click this button to reveal the filter’s criteria.
The first active filter specifies the time range (field name @timestamp). When you access the preset investigation, the time range is set to one hour (the most recent hour).
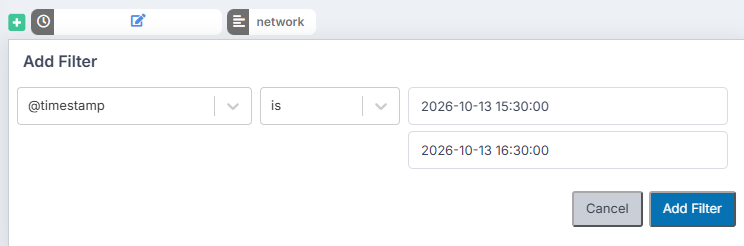
The second active filter (field name datatype) is set to is network. This restricts the information shown to only network-related data, which is appropriate filter criteria for our example investigation.
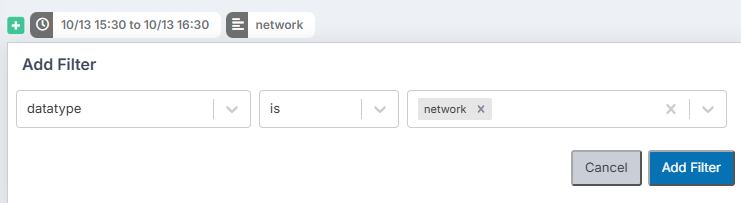
In our example investigation, we want to find internal network traffic communicating with non-US public IPs between two dates. To refine the investigation, let’s first modify the time range. To do so, you can either:
- Modify the filter criteria (the dates) of the @timestamp filter (as seen in the preceding image), and then click Add Filter.
-or-
- Click one of the preset time range buttons in the upper-right corner of the page.
For example, to view data for the maximum time range available, you could click the  preset time range option. Doing so would cause much more data to be displayed, as seen in the following image.
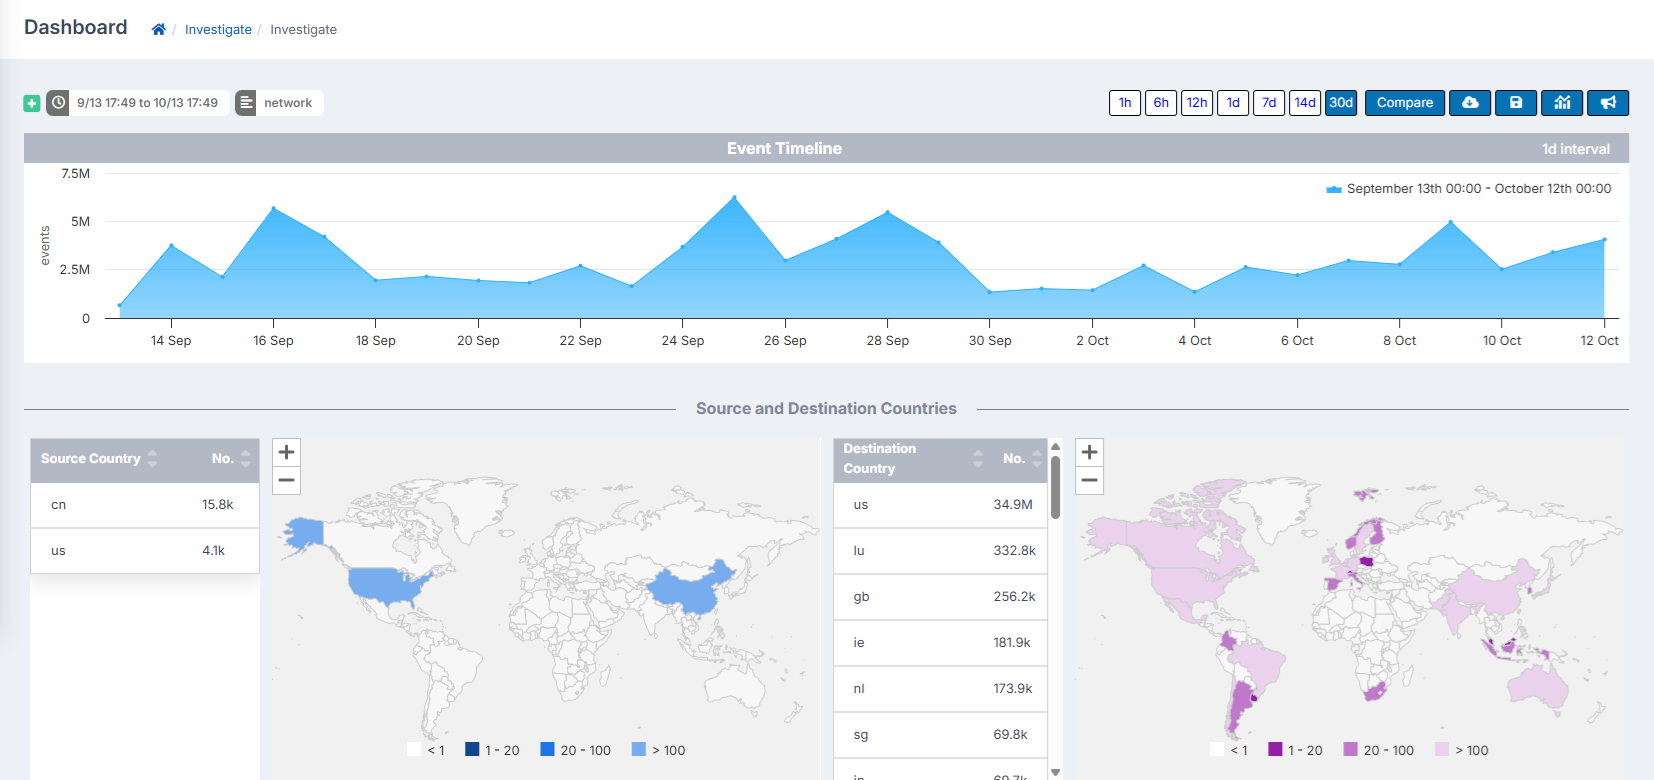
In our example, we want to find internal network traffic communicating with non-US public IPs. To refine the investigation to display only this information, three filters need to be added to the investigation. The next two sections deal with adding these filters.
Example Investigation: Adding the src_ip.private Filter
In our example, we want to look only at communications whose source is the internal network. To filter the investigation in this way, set the src_ip.private filter to is true.
The field value src_ip.private is named based on the element src_ip representing “source IP,” and the element private representing “private network” (an IP address can either be a public IP address, or a private network). By setting this filter to is true, the investigation will return data related to source IP addresses on a private network.
Here are two ways that you can add the src_ip.private filter:
- Manually add the filter: In the upper-left corner of the page where the filters are shown, click the button, then select values as seen in the following image, and then click Add Filter.
tip
Type ahead! The list of possible options for some fields can be very long. Before selecting an option from the list, you may want to enter, in the field’s text box, several letters of the filter value you want.
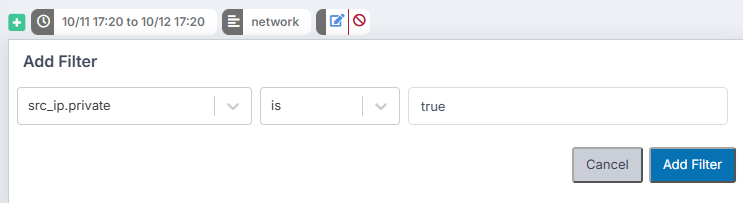
- Add the filter via the corresponding events table: At the bottom of the Investigate results page, the corresponding events table appears. This table contains all of the events relevant to the current filtering criteria of the investigation.
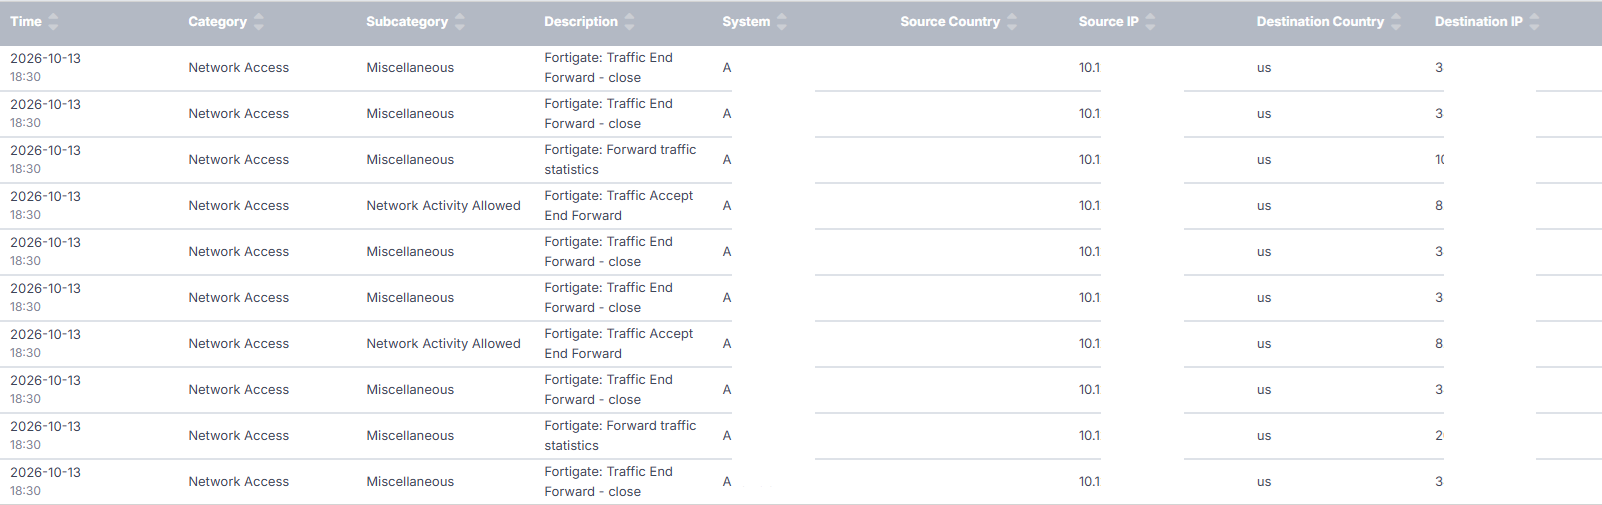
Select any row in this table to expand the event, revealing its details.
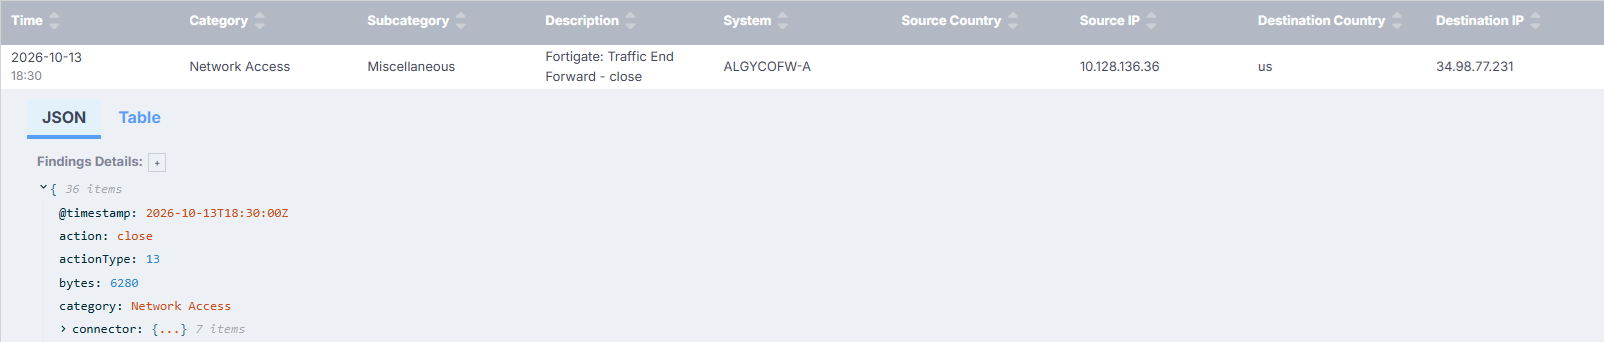
Next, click Table to reveal the event’s Table section.
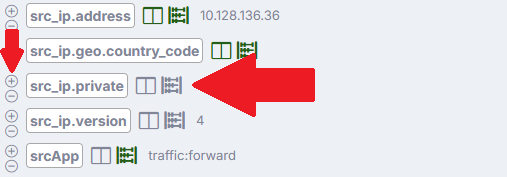
In the Table section, scroll down to find the src_ip.private field value.
-or-
Each row in the Table section has a number of controls to help you refine investigation results. For the purposes of our example, we want to add the src_ip.private field value as inclusive by clicking the plus button in its row (indicated by the smaller red arrow in the preceding image). Clicking this plus button will immediately add the filter with the criteria we require to the investigation.
Consider these additional controls that are available in the Table section. With these tools, you can refine and interrogate event data in a multitude of ways.
- You can select the plus or minus button beside any field value to add it as an inclusive or exclusive filtering criteria.
- You can select the
 button beside any field value to toggle its inclusion as a column in the table of events. This can make it easier to find relevant information when scrolling through results. If the button is green (
 ), the value will be included as a column. If the button is gray (), the value will not be included.
- You can select the
 button beside any field value to toggle its inclusion as a subsection within the Field Summary section. This is an excellent way to display summary information for comparison. If the button is green (
 ), the subsection will be included. If the button is gray (), the subsection will not be included.
With the src_ip.private filter criteria added, the Investigate results page shows only data related to communications whose source is the internal network.
Next, let’s add the other two filters needed to fulfill the requirements of our example investigation.
Example Investigation: Adding the dst_ip.private and dst_ip.geo.country_code Filters
In our example, we want to look only at communications whose destinations are non-US public IPs.
First, let’s add a filter to limit the data to public destination IPs. To filter the investigation in this way, set the dst_ip.private filter to is false.
The field value dst_ip.private is named based on the element dst_ip representing “destination IP,” and the element private representing “private network” (an IP address can either be a public IP address, or a private network). By setting this filter to is false, the investigation will return data related to public destination IP addresses.
Here are two ways to add the dst_ip.private filter:
- Manually add the filter: In the upper-left corner of the page, click the button, then select values as seen in the following image, and then click Add Filter.
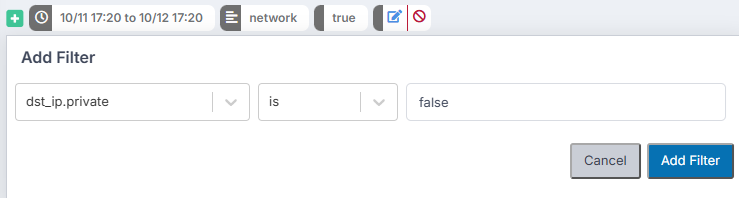
- Add the filter via the corresponding events table: As before, access the Table section of an event in the corresponding events table. Then, scroll down to find the dst_ip.private field value.
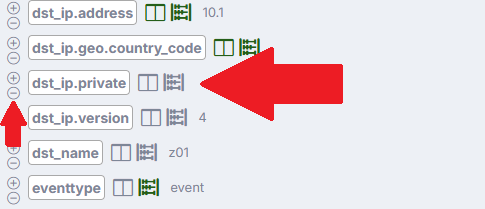
For the purposes of our example, we want to add the dst_ip.private field value as exclusive by clicking the minus button in its row (indicated by the smaller red arrow in the preceding image). Clicking this button will add the filter immediately with the appropriate criteria selected. With this method, the filter is added with the criteria is not true instead of is false.tipWhile both the is not true and is false options will return the same data, the is false option is preferred, as the is operator will provide faster query results. You can modify the criteria is not true to is false by editing the filter.
-or-
Next, let’s add a filter to limit the data to non-US destination IPs. To filter the investigation in this way, set the dst_ip.geo.country_code filter to is not us. This filter will exclude US destination country results from the investigation. Let’s look at two ways to add this filter:
- Manually add the filter: In the upper-left corner of the page, click the button, then select values as seen in the following image, and then click Add Filter.
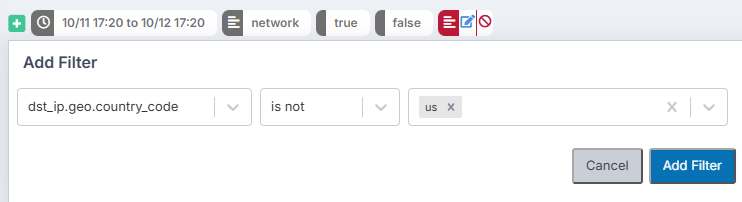
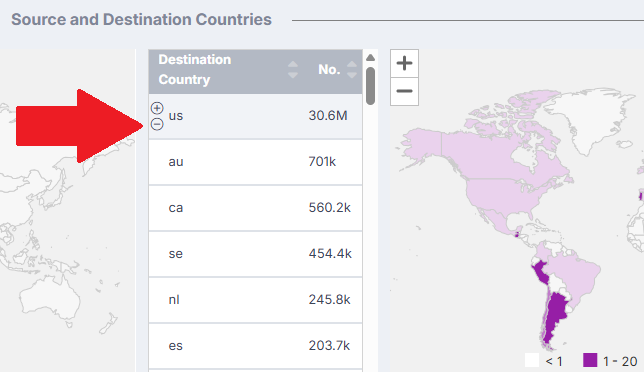
- Add the filter via the Destination Country table: A quick way to add this filter is to use the controls in the Destination Country table. To add the filter, simply hover over the us row in the table, and then click the minus button that appears. This will create the same filter seen in the preceding image.
-or-
With the three filters added, the investigation has been limited to the data we wanted: internal network traffic communicating with non-US public IPs between two dates.
Next, let’s consider how this example investigation can be further modified to drill down on specific data.
Example Investigation: Focusing Investigation Data
Let’s consider what we can learn from the data in our example investigation. Important information about the investigation data is found in the tables in the Field Summary section.
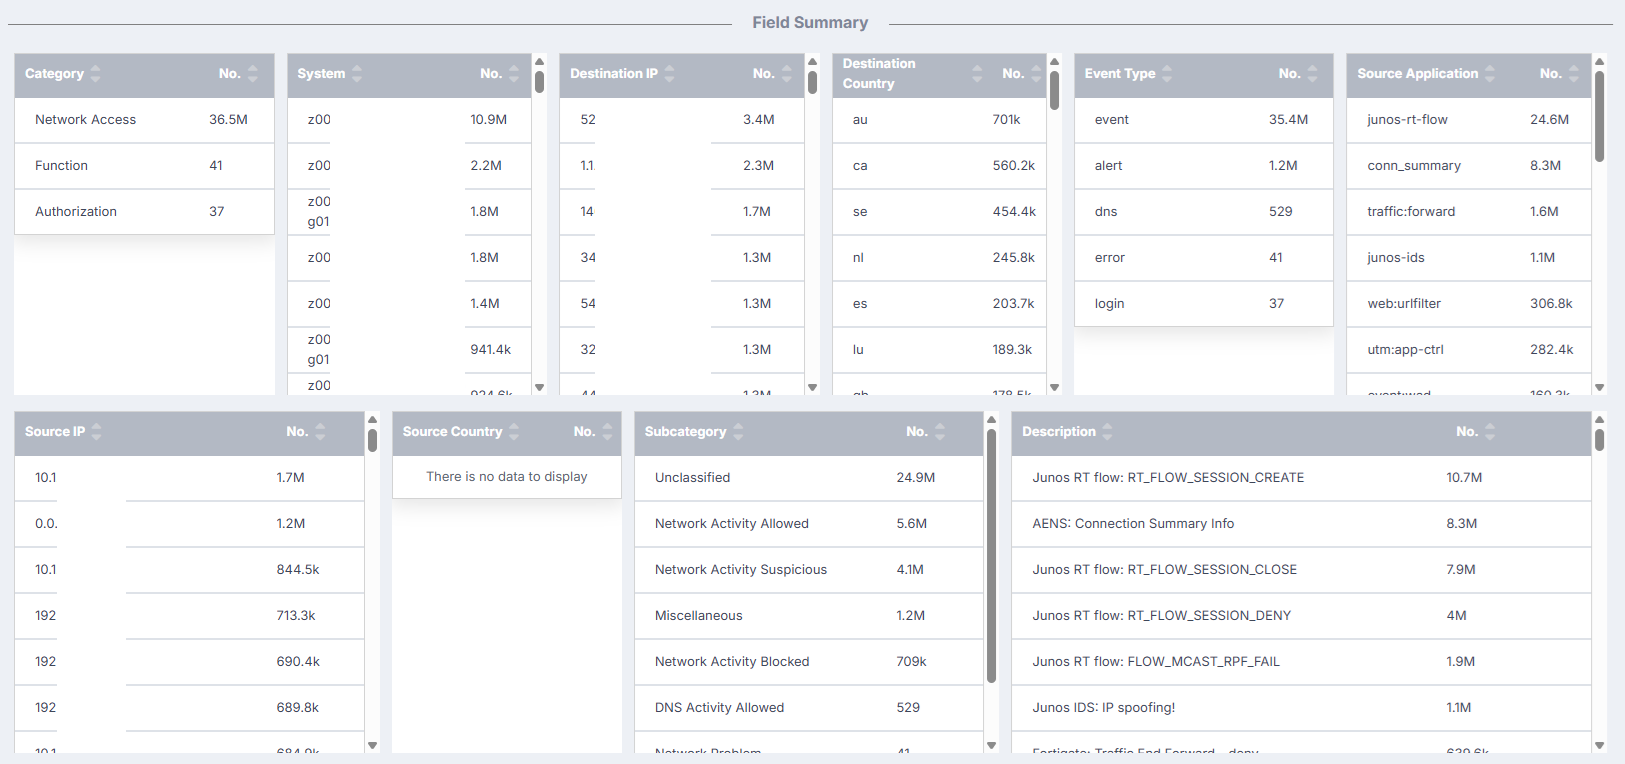
The information in the field summary tables reveal trends in data, and can be used to further drill down to reveal more specific information. For example, in the Destination County table, the destination countries are listed by numbers of communications in descending order, allowing you to see at a glance which countries are communicated with most and least. If you want to further drill down and focus on data associated with a specific country in the list, you can hover over that country’s row in the Destination County table, and then select the plus button to add it as an inclusive filter.
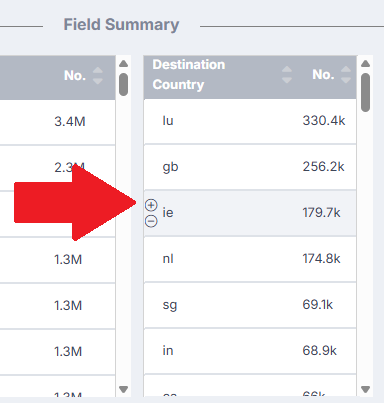
Doing so will add a new filter that limits the data shown on the Investigate results page to connection data associated with this specific destination country.
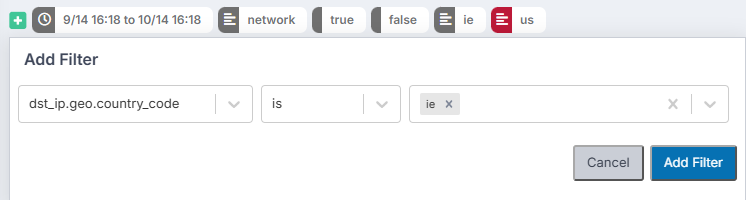
Note that you can add additional destination countries to this filter, expanding the investigation to as many additional destination countries as you want. To do so, simply access the filter’s edit window, then enter a country code …
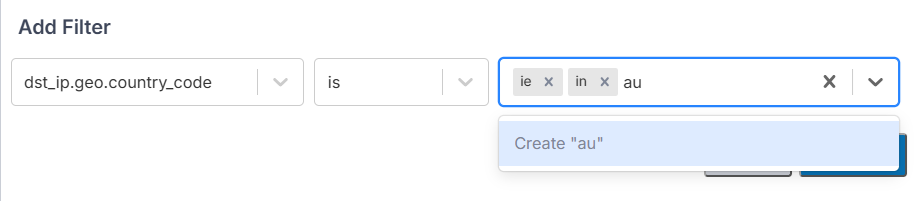
… then press Enter …
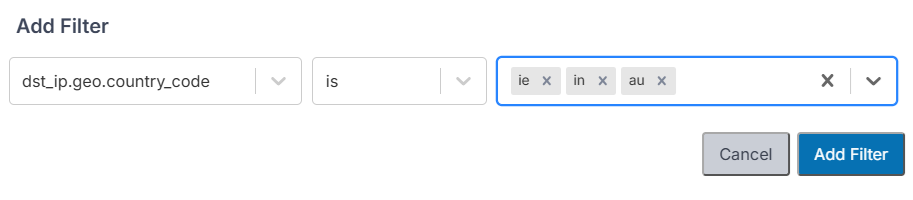
… and then click Add Filter. The data on the Investigate results page will update to include data related to all of the selected destination countries.
This method of modifying filters can be used in many situations.
Next, let’s say you want to further filter the results so that only data related to alerts is displayed. To do so, in the Field Summary section, in the Event Type table, hover over the alert row, and then select the plus button that appears. This will add alert data as an inclusive filter.
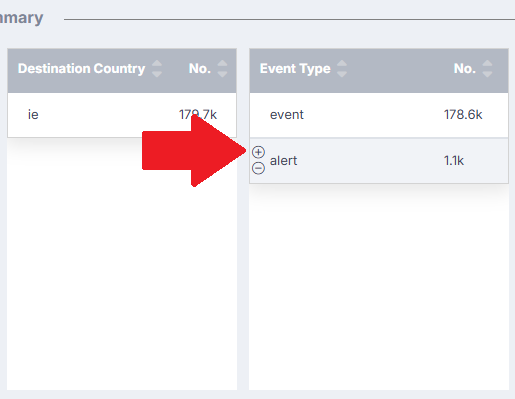
Doing so will add a new filter that further limits the data shown on the Investigate results page to data associated with alerts.
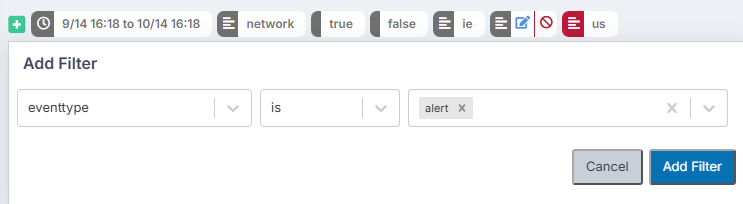
With all of these filters applied to the investigation, the number of results that appear on the Investigate results page should begin to be more manageable and understandable. For example, you could refer to the Destination IP table in the Field Summary section to see which destination IPs receive the most communications, and could further refine the investigation results by filtering on one or more of the destination IPs.
Add filters to drill down further into specific data, and, if you need to broaden your focus, delete an existing filter by clicking the  button that appears when you hover over the filter. Keep in mind that narrowing the time range of an investigation is often the best way to derive a manageable quantity of data.
By adjusting filters and time ranges, you can find specific events in the corresponding events table, the large table at the bottom of the Field Summary section. This table displays all events related to the investigation. As noted previously, you can click any row in the table to expand the Findings Details of that event. This provides extremely detailed information about the selected event.
Utilizing Successful Investigations
When you have achieved successful investigation results through filtering, there are a number of features you can use to compare, save, and publish your investigation. The following functions are accessed by clicking the buttons in the utility panel, found in the upper-right corner of the Investigate results page.
- Compare data: To compare the data in the selected timeline to a second timeline, click Compare. When you do, the Event Timeline section displays a second graph, and counts that were displayed in the Field Summary section are replaced with the difference between counts in the compared timelines. The second timeline displayed will span the range of dates directly preceding the currently selected range of dates. For example, if the original data spanned a 14 day range from 06/17/24 to 06/30/24, the compared data will span the 14 days prior to that range: 06/03/24 to 06/16/24. When comparing data, you can download data, create a report module with the data, or add the data to a daily email summary. To close the comparison and return to the original data, click Clear.
- Download data: To download the data for further processing or archiving, click
 . You can download the data in the CSV or JSON format. If the Include aggregates checkbox is selected, the downloaded ZIP file will include a JSON Source File containing the aggregate counts from the boxes in the Field Summary section. If the Include manifest checkbox is selected, the downloaded ZIP file will include a JSON Source File containing the query details. The maximum download size is 10,000 events.
- Save investigation: If you have modified filters and want to save your changes, click
 . Then, in the Save Investigation window, modify the Display Name and Description as needed. If you want the investigation to be visible to others within your organization, select the share with your organization checkbox; if this checkbox is cleared, the saved investigation will only be visible to you. If you want the saved investigation to always display time relative to when it is accessed, meaning that it will always display data in the selected time range up to the present, select the relative time checkbox. If you instead want the investigation to always display data in the specific range of time shown when it is saved, clear the relative time checkbox. If you are saving a modified version of a saved query, you can click Update Query to overwrite the saved query, or you can click Create Query to create a new, separate saved query. If you are saving a modified preset investigation, you must create a new query. To update the investigation with your changes, click Update Query.
- Create a report module: Investigations can be added to custom reports through the creation of a report module, which can then be configured and added to a report template. To create a report module, click
 . Then, in the Reporting window, modify the Title and Description as needed. If you want ActiveEye to open a new tab where you can create a report template containing the report module, select the create report now checkbox. For more information on using report templates, see the Adding a new report template section of the Reports topic. To create the report module, click Create Module.
note
The report module you create will be separate from the investigation used to create it. Further modifications to the investigation will not affect the report module, and modifications to the report module will not affect the investigation.
- Add the investigation to a daily email summary: To add the investigation to a daily email summary, click
 . Then, in the Daily Email Summary window, select the name of the daily email summary to which you want to add the investigation. When you make the selection, the investigation is added to the daily email summary immediately. If you want to edit a daily summary, click Edit Daily Email Summaries. For more information, see the Daily Email Summary topic.
Examples of fields
Here are some examples of fields commonly used as filtering criteria or included in the Field Summary section, and explanations of their purposes.
- dst_name (Destination Name): Filter on this field to limit events returned to only those involving a particular destination. This can give you an overview of the types of traffic that destination receives.
- srcApp (Source Application): You could filter on this field to see all events associated with a specific service, to better understand the overall activity of the service.
- source_ip.geo.country_code: Filter on this field to view events originating from a specific country, allowing you to focus on potentially malicious activity from particular geographic locations.
- duser (Destination User): Filter on this field to view events related to a specific user, to see what other actions the user took near the time of an action you are investigating. This can be useful in determining what the user was trying to accomplish.
- subcategory (or actionType): These fields usually report the success or failure of an event, informing you of the results of intended actions.
- action (and desc): The action and description fields will help inform you of what triggered the alert. These values can be different, but tend to be similar messages written with different verbiage. You should use both fields for a more complete view.