Google Security Command Center (SCC)
Prerequisites
Completing this setup requires certain Google Cloud Platform (GCP) IAM roles.
- Security Center Admin Viewer: This role grants access to the Security Command Center dashboard.
- Security Center Admin: This role allows the user to enable Security Command Center API notifications.
- Organization Administrator: This role allows the user to grant appropriate roles to the notifications service account or GCP tool account.
Creating the SCC Service Connector
- In ActiveEye, in the left pane, click Admin, and then click Service Connectors.
The Service Connectors page appears.
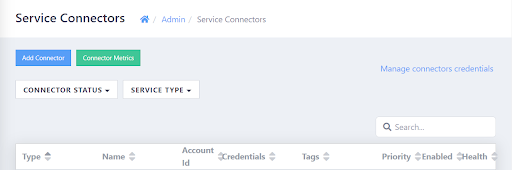
- In the upper-left corner of the page, click Add Connector.
A list of service connectors appears.
- Scroll down to the SECURITY MANAGEMENT section, and then, in the Google Cloud Security Command Center subsection, click the Add Connection button.
The Add Connector Account page appears. - In the Display Name box, enter a unique name.
- Optionally, modify the priority level in the Priority box. Raising or lowering the priority will increase or decrease the visibility of alerts related to this service connector.
- If you do not want data ingestion to begin immediately once cloud accounts have been configured, clear the Enable Account checkbox. Otherwise, leave the checkbox selected.
- Click Add.
The Google SCC service connector is created, and the page is refreshed. - Copy the values in the Event Ingestion URL (Read Only) and Event Ingestion Token (Read Only) boxes. You will use these values in a subsequent procedure.
GCP Configuration
Enabling API
Follow these steps to enable an API for a project using the console.
- Click this link to access the GCP API Library.
- From the projects list, select the project in which you want to enable this API.
- In the Search for APIs & Services box, enter Security Command Center API, and then press Enter.
Search results appear. - In the search results, select Security Command Center API.
The Product details page appears. - Click Enable.
Configuring the Pub/Sub to Forward Logs
To enable log forwarding, perform the following steps:
- Create a new topic in the Pub/Sub console by following the steps in this GCP procedure: Create a topic. As you complete the linked procedure, enter a unique name in the Topic ID box, but do not modify the other default options.
- Create a new push subscription in the Pub/Sub console by following the steps in this GCP procedure: Push subscription.
As you complete the linked procedure, enter information as follows:
- When making a selection in the Select a Cloud Pub/Sub topic list, select the topic that was created in step 1.
- When specifying an endpoint URL, use the Event Ingestion URL for the ActiveEye SCC service connector. If your push configuration supports custom HTTP headers, add the
Authorizationheader with the valueBearer <token>, replacing<token>with the Event Ingestion Token. Otherwise, append the token to the endpoint URL as a query parameter:<Event Ingestion URL>?api-key=<token>. If the URL already contains a query string, use&api-key=<token>instead.
A Pub/Sub topic and subscription should be created for each service connector created. Be sure to use logical naming conventions when creating these items.
Granting Permissions for the Pub/Sub
To create a NotificationConfig that reads the Security Center findings and puts them into the Pub/Sub, permissions need to be granted to the tool performing this function.
To grant the permissions, follow the steps within Step 2: Set up gcloud CLI account permissions in this GCP procedure: Setting up a Pub/Sub topic. Ignore the steps within Step 1: Set up Pub/Sub, as you completed those operations in the last procedure.
As you complete the linked procedure, when you reach the Grant the gcloud CLI account a role that includes all of the securitycenter.notification permissions step, grant the role at the organization level. You can grant either the roles/securitycenter.notificationConfigEditor or roles/securitycenter.admin role. If you want to grant the roles/securitycenter.notificationConfigEditor role, the code you enter will look like this:
              gcloud organizations add-iam-policy-binding $ORGANIZATION_ID \
                 --member="user:$GCLOUD_ACCOUNT" \
                 --role='roles/securitycenter.notificationConfigEditor'
Creating a NotificationConfig
The NotificationConfig includes a filter field that limits notifications to useful events. This field accepts all of the filters that are available in the Security Command Center API findings.list method.
Each organization can have a limited number of NotificationConfig files. Also, the Organization Administrator IAM role is needed to grant appropriate roles to the notifications service account or GCP tool account.
To create a NotificationConfig for all findings, complete the following steps:
- Select the project in which the Security Command Center API was enabled.
- In the upper-right corner of the toolbar, click the Activate CloudShell icon, which looks like this: >_
The CloudShell Terminal pane appears. - Set the organization name by running the following command (replace [organization ID] with your organization ID):
export ORGANIZATION_ID=<i>[organization ID] - Set the email of the account used to run GCP tool commands by running the following command (replace [your-username@email.com] with your email address):
export EMAIL=<i>[your-username@email.com]
- Create the NotificationConfig by running the entirety of the following command. Before running it, replace [organization-id], [project-id], and [topic-id] with the neccessary values, and replace [notification-name] with a name of your choice that does not contain spaces.
              # The numeric ID of the organization
              ORGANIZATION_ID=[organization-id]

              # The topic to which the notifications are published
              PUBSUB_TOPIC="projects/[project-id]/topics/[topic-id]"

              # The description for the NotificationConfig
              DESCRIPTION="Notifies for active findings"

              # Filters for active findings
              FILTER=""

              gcloud scc notifications create [notification-name] \
                --organization "$ORGANIZATION_ID" \
                --description "$DESCRIPTION" \
                --pubsub-topic $PUBSUB_TOPIC \
                --filter "$FILTER"
Notifications are now published to the specified Pub/Sub topic. To publish notifications, Security Command Center uses an organization-level service account in the form of service-org-organization-id@gcp-sa-scc-notification.iam.gserviceaccount.com with the role securitycenter.notificationServiceAgent. This organization-level service account role is required for notifications to function.